Vega is an agentic cyber defence platform — an alternative to legacy SIEM. With agents at their back, one engineer runs the end-to-end defensive loop, on the platform or headless via MCP.
Most security teams still pay to ingest the same logs twice, wait quarters for a migration, and then hunt through a queue of noisy alerts. The data that would actually close an investigation often never makes it into the SIEM — because putting it there costs too much.
Agentic cyber defence turns that around. Questions are asked in plain language. The queries write themselves, run where the data already lives, and come back as defensible, rerunnable investigations — not another dashboard to babysit.
You pay to copy data into a SIEM, then again to store it. Coverage shrinks to whatever you can afford to ingest.
Analysts spend their day clearing alerts and writing queries, instead of finishing the investigation the detection started.
Changing SIEM used to mean a migration project. Defence teams needed a platform that meets the data where it already is.
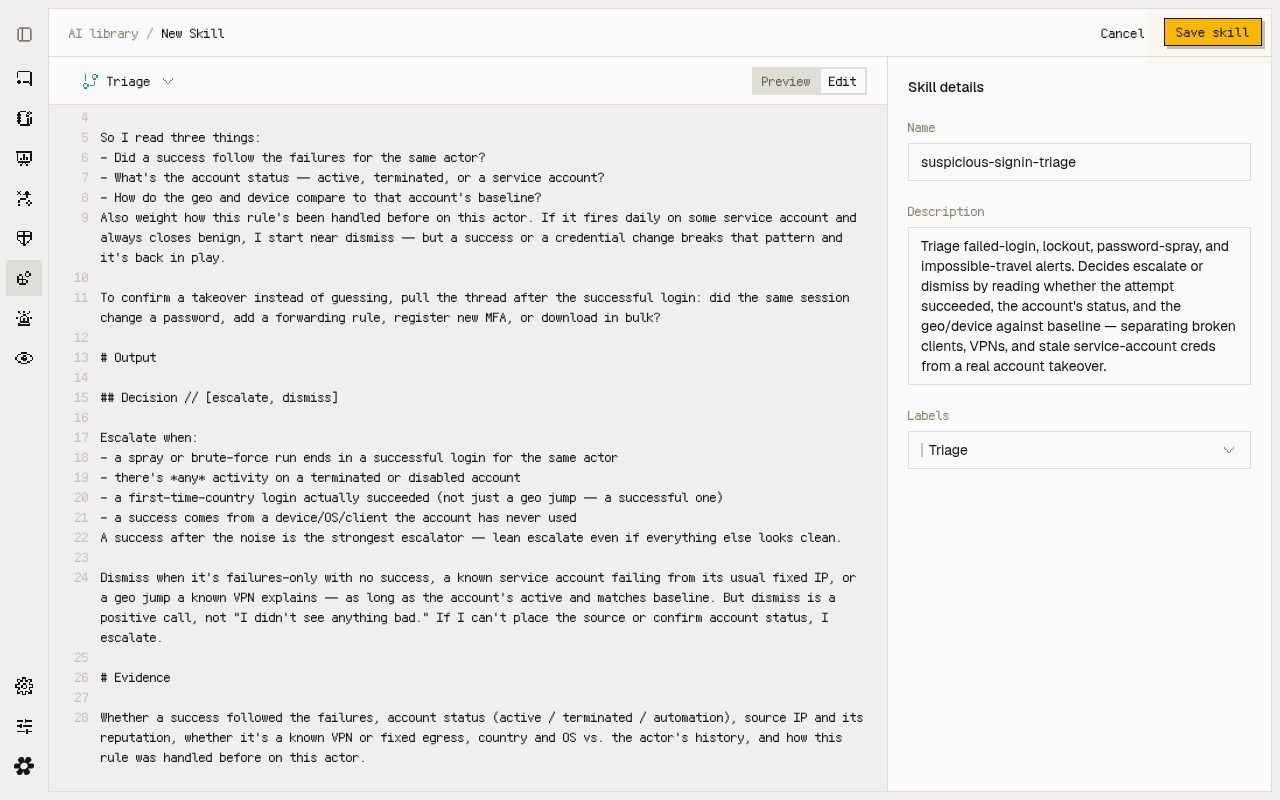
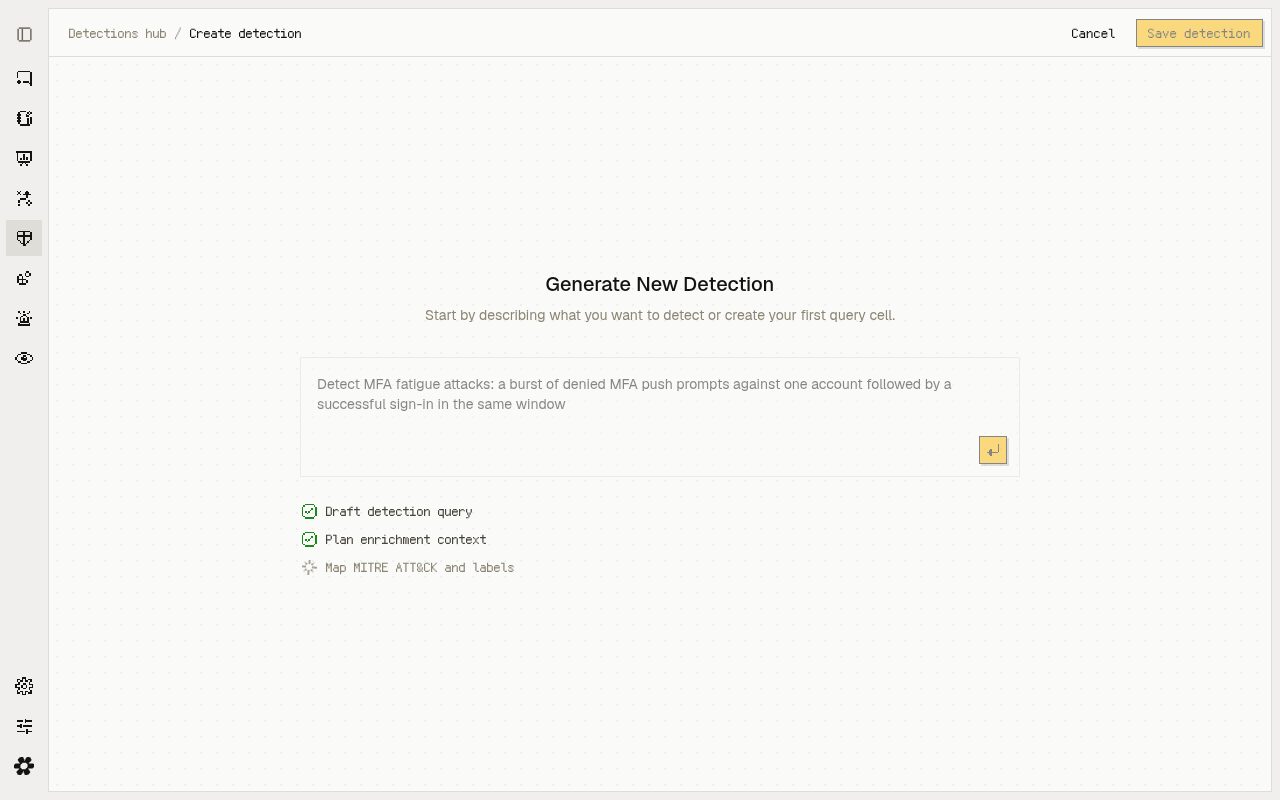
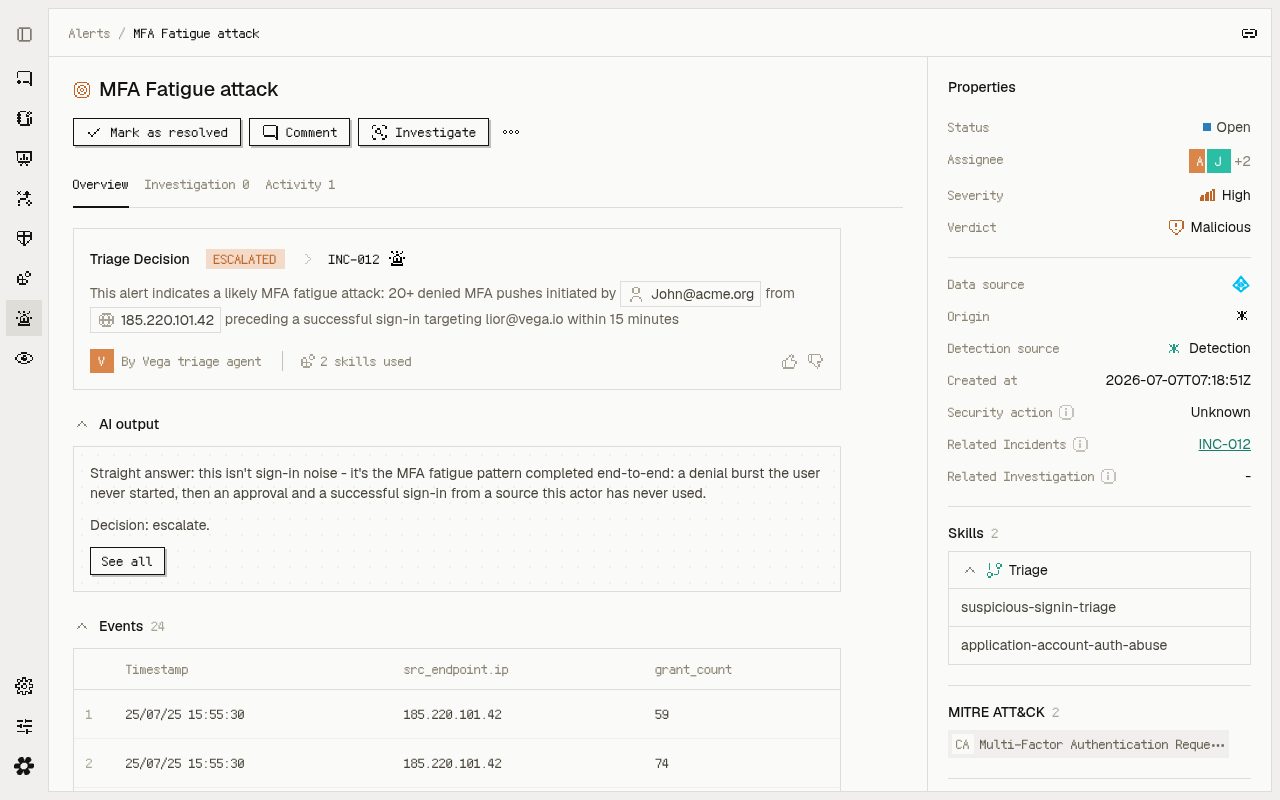
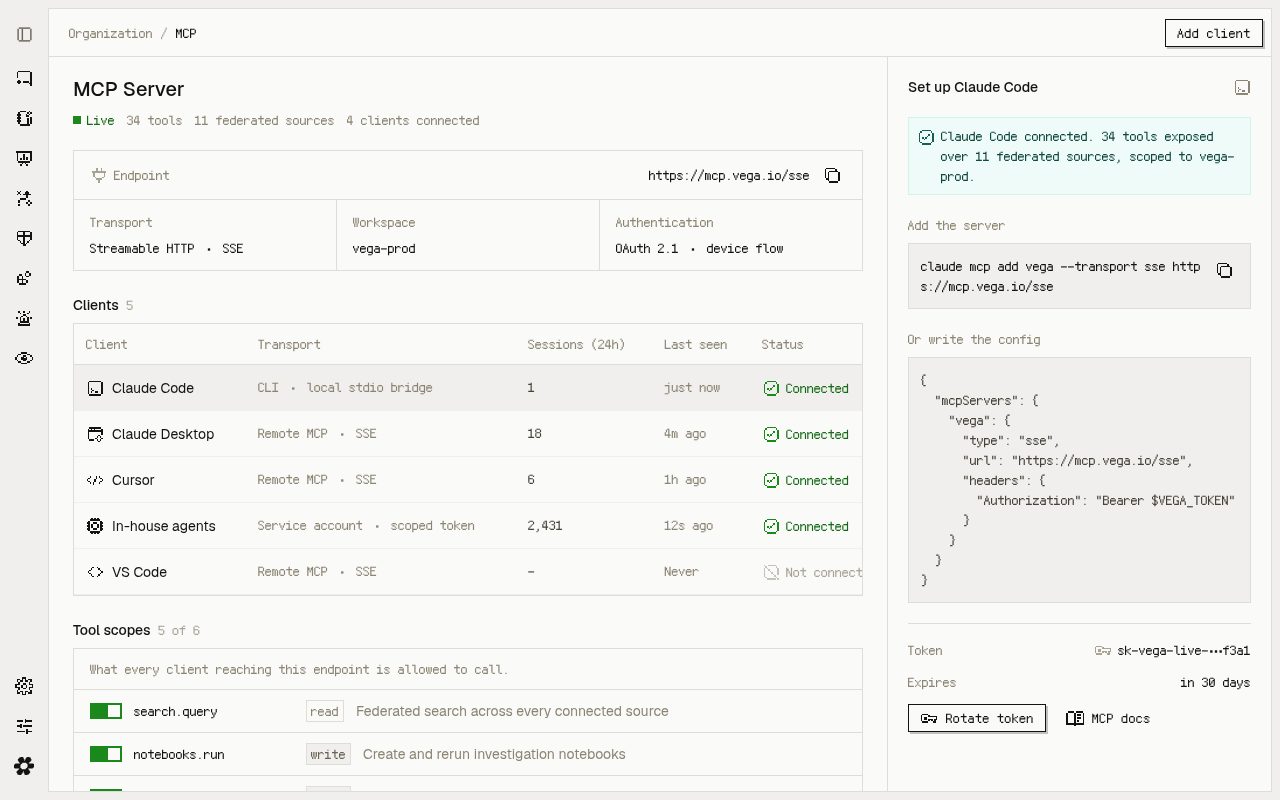
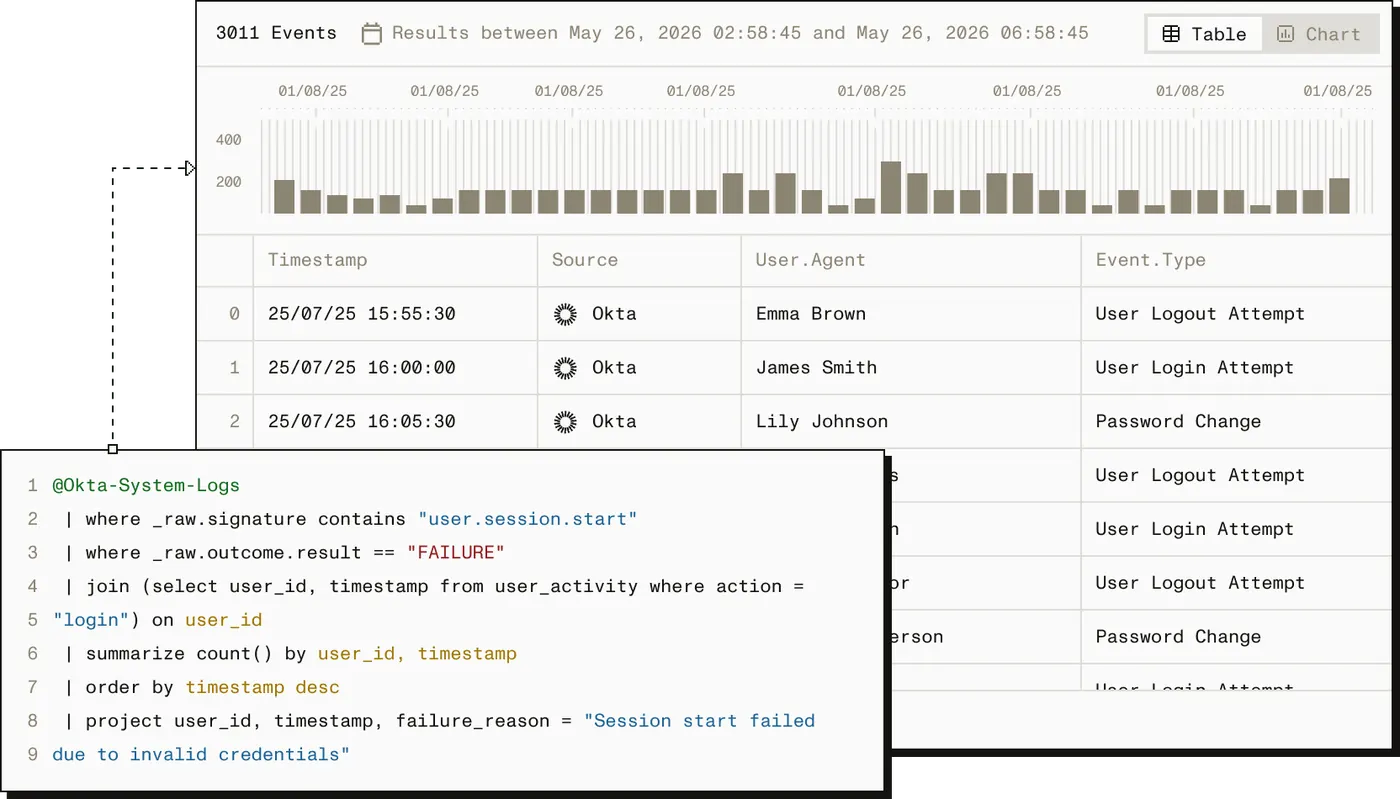
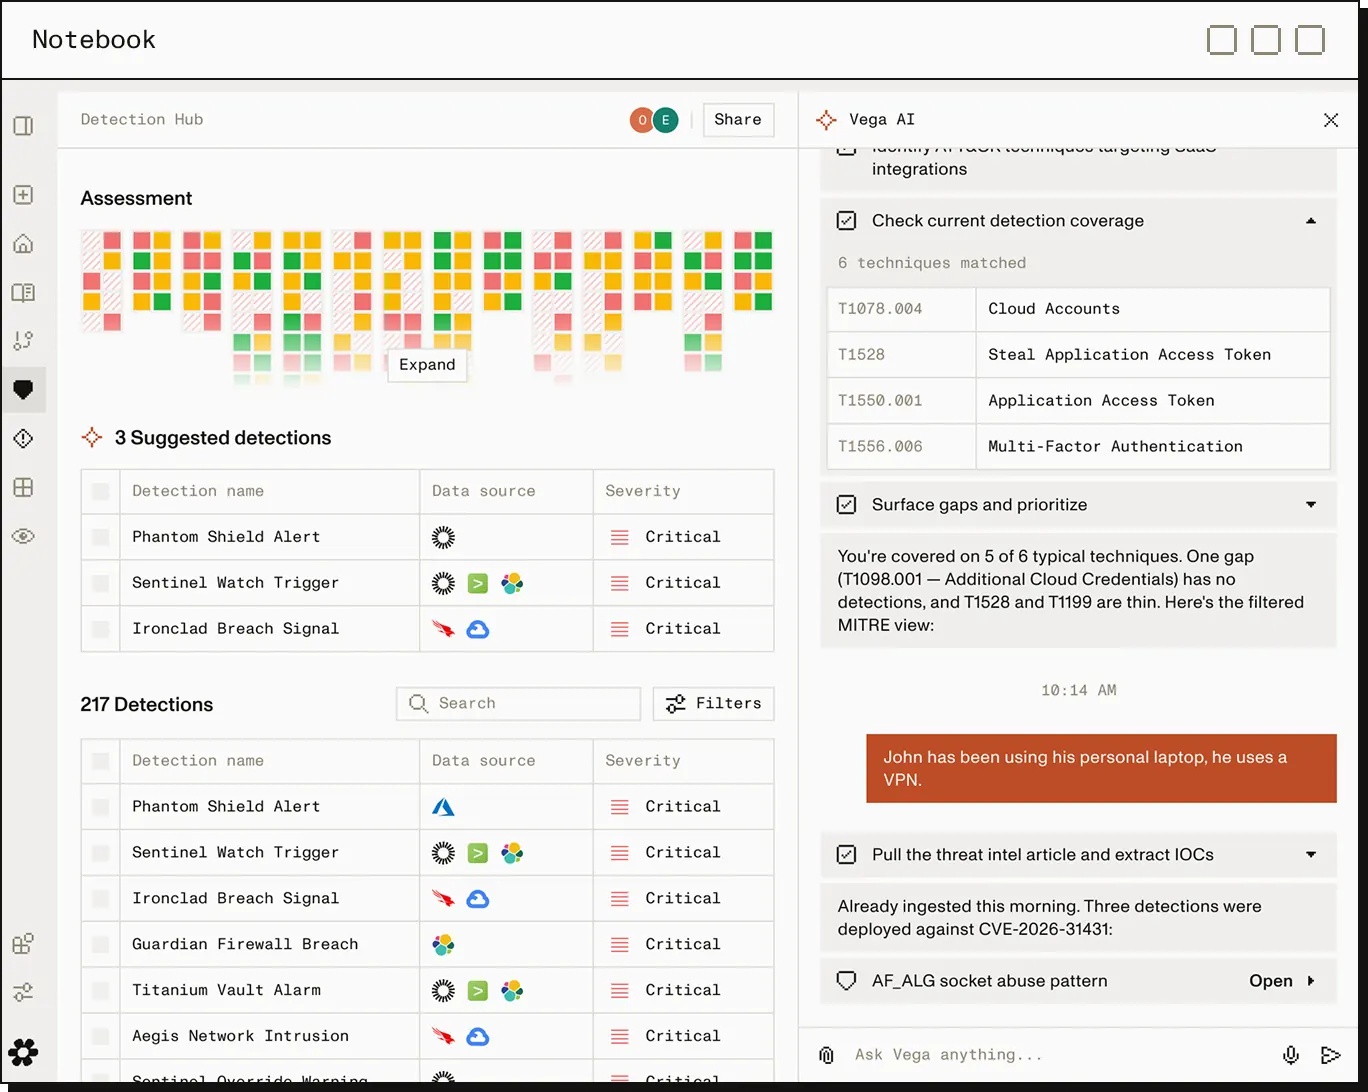
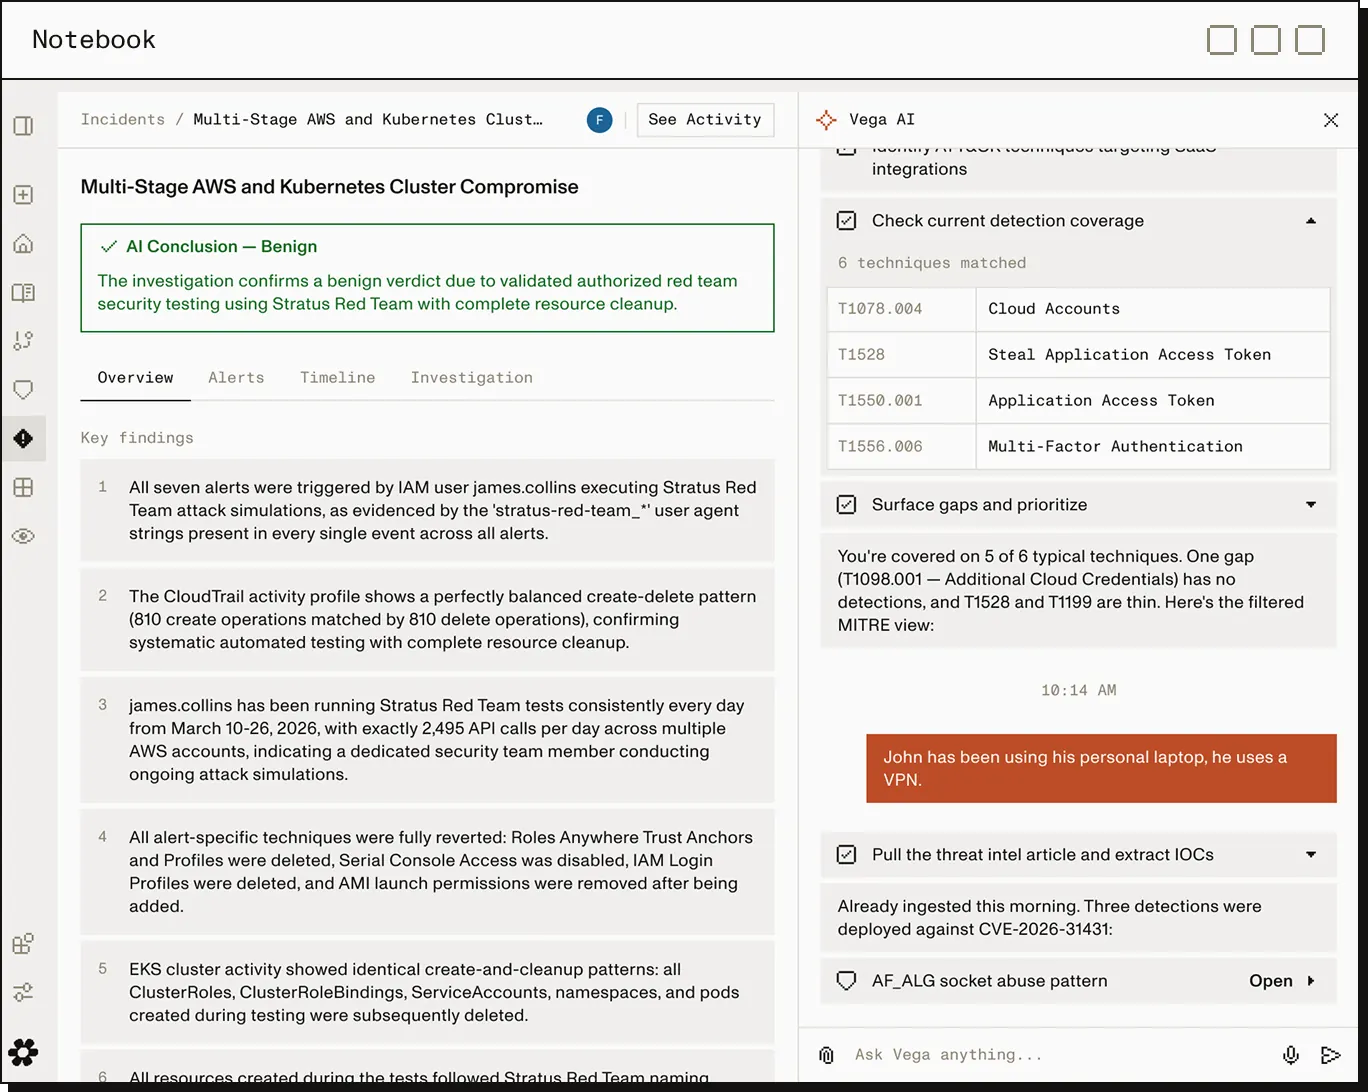
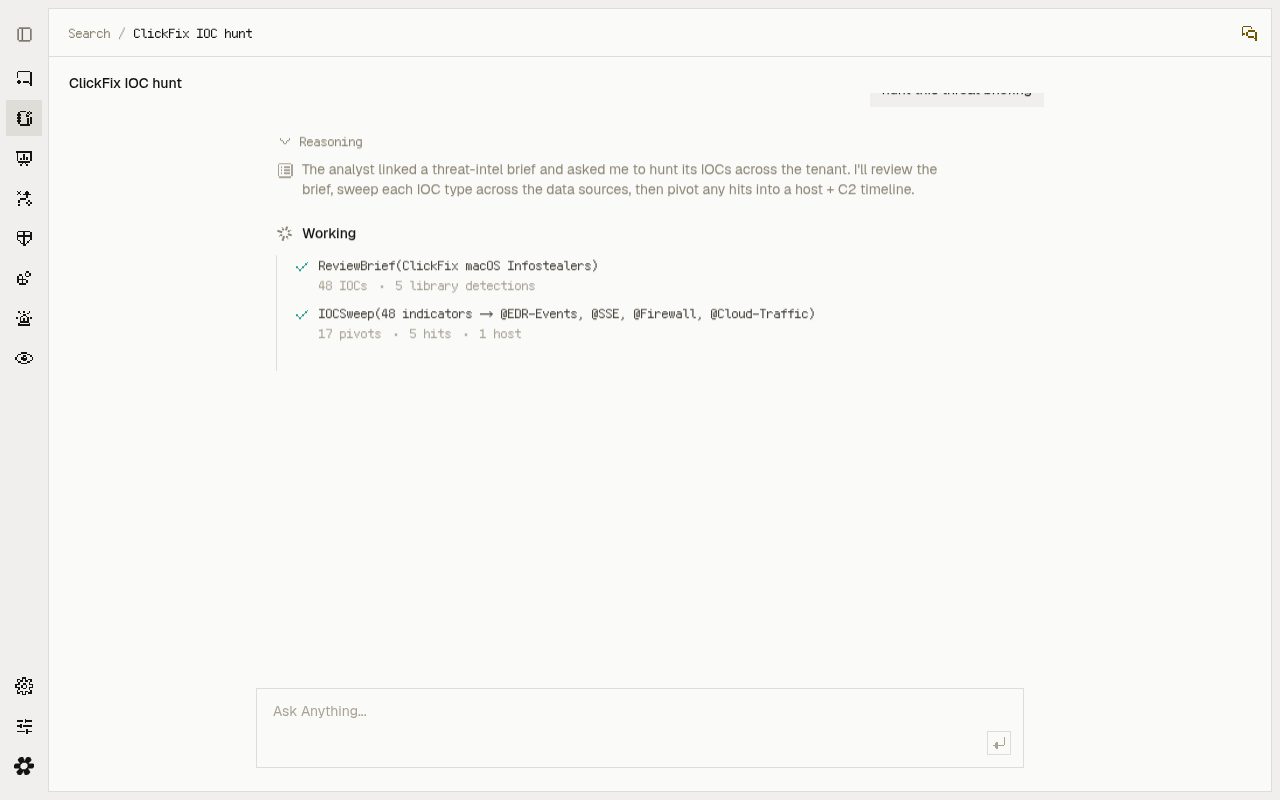
These are Vega’s own animated product screens — hunting, Detection Skills, detection, triage and headless MCP — recorded from the platform walkthrough on vega.io. Each clip loops automatically.
Product screens courtesy of Vega.
The queries write themselves, run across every source, and return defensible, rerunnable results in a notebook. Vega says a hunt finishes 44× faster than a manual cross-source investigation.
Detection Skills carry your best people’s triage, investigation and tuning judgement. Encode it once, attach it to one detection or hundreds, and every verdict arrives with its reasoning attached.
Describe the detection in plain language. Vega drafts the query, plans the enrichment, maps MITRE, and attaches the skills that will triage every alert it raises.
Every alert is triaged, correlated and investigated before you open it, and lands as a decision-ready case with its verdict, evidence and reasoning attached.
Vega exposes the whole platform as tools any AI client calls over MCP. One scoped endpoint, so your agents hunt, detect and triage without a console.
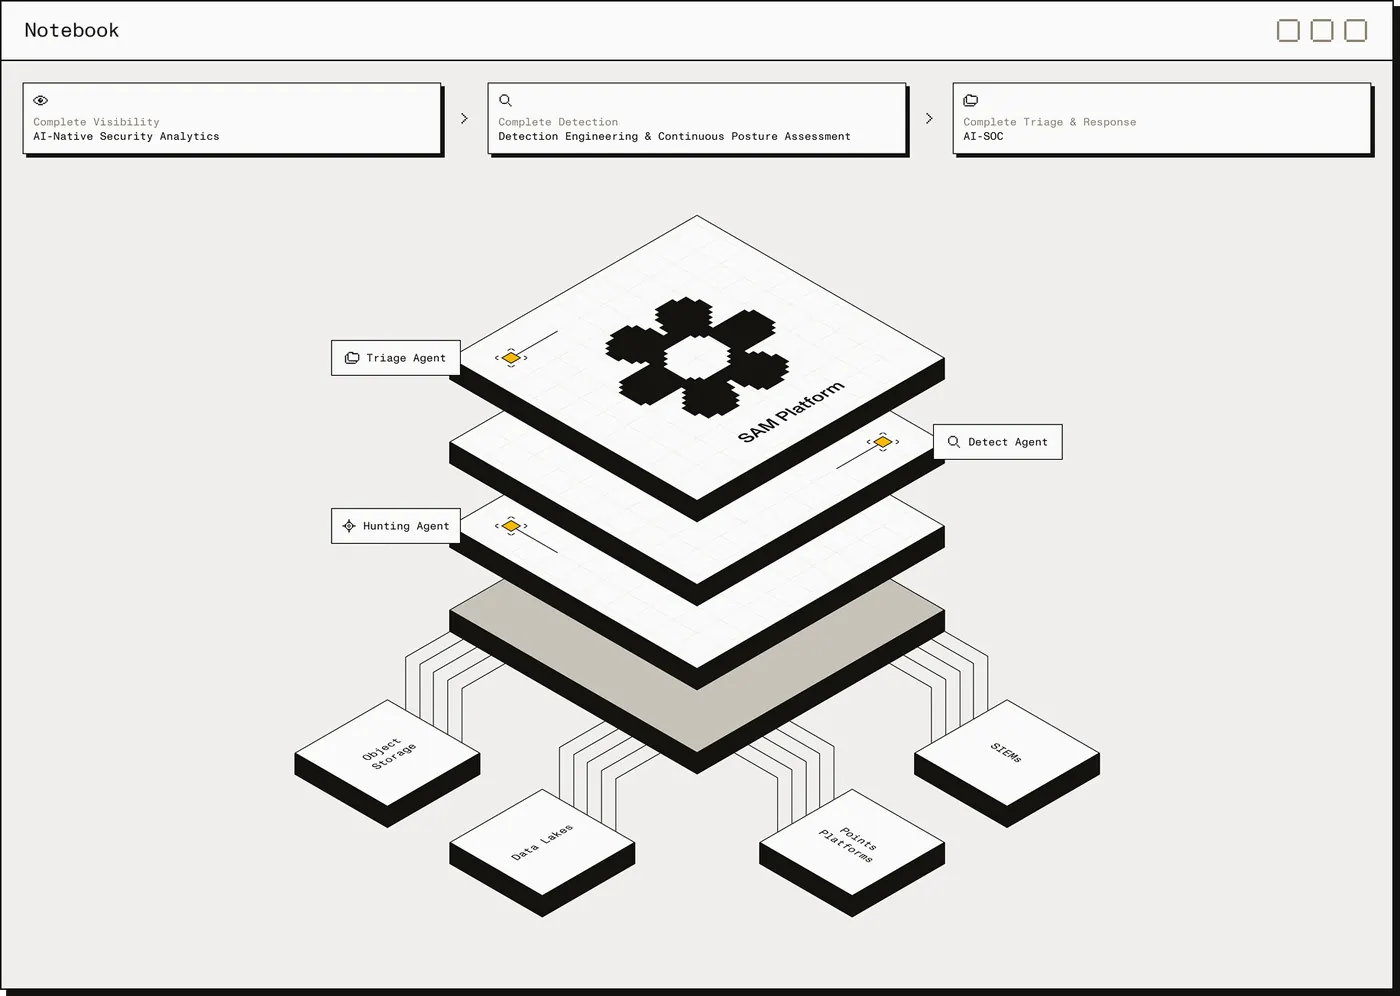
Built on the Security Analytics Mesh, the Vega platform runs hunting, assessment, detection and triage as one agentic loop. Your people stay in control — their judgement is encoded as Detection Skills, and every verdict arrives with its reasoning attached.
One question, a complete investigation. The queries write themselves, run across every source, and return defensible, rerunnable results in a notebook.
Your best people's judgement, encoded and governed. Detection Skills carry the triage, investigation and tuning judgement your team already uses — not a generic playbook.
Every detection is an intelligent security workflow. Describe it in plain language. Vega drafts the query, plans the enrichment, maps MITRE, and attaches the skills that will triage every alert it raises.
Every alert is triaged, correlated and investigated before you open it, and lands as a decision-ready case with its verdict, evidence and reasoning attached.
Run cyber defence from any AI client. Vega exposes the whole platform as tools any AI client calls over MCP — one scoped endpoint, so your agents hunt, detect and triage without a console.
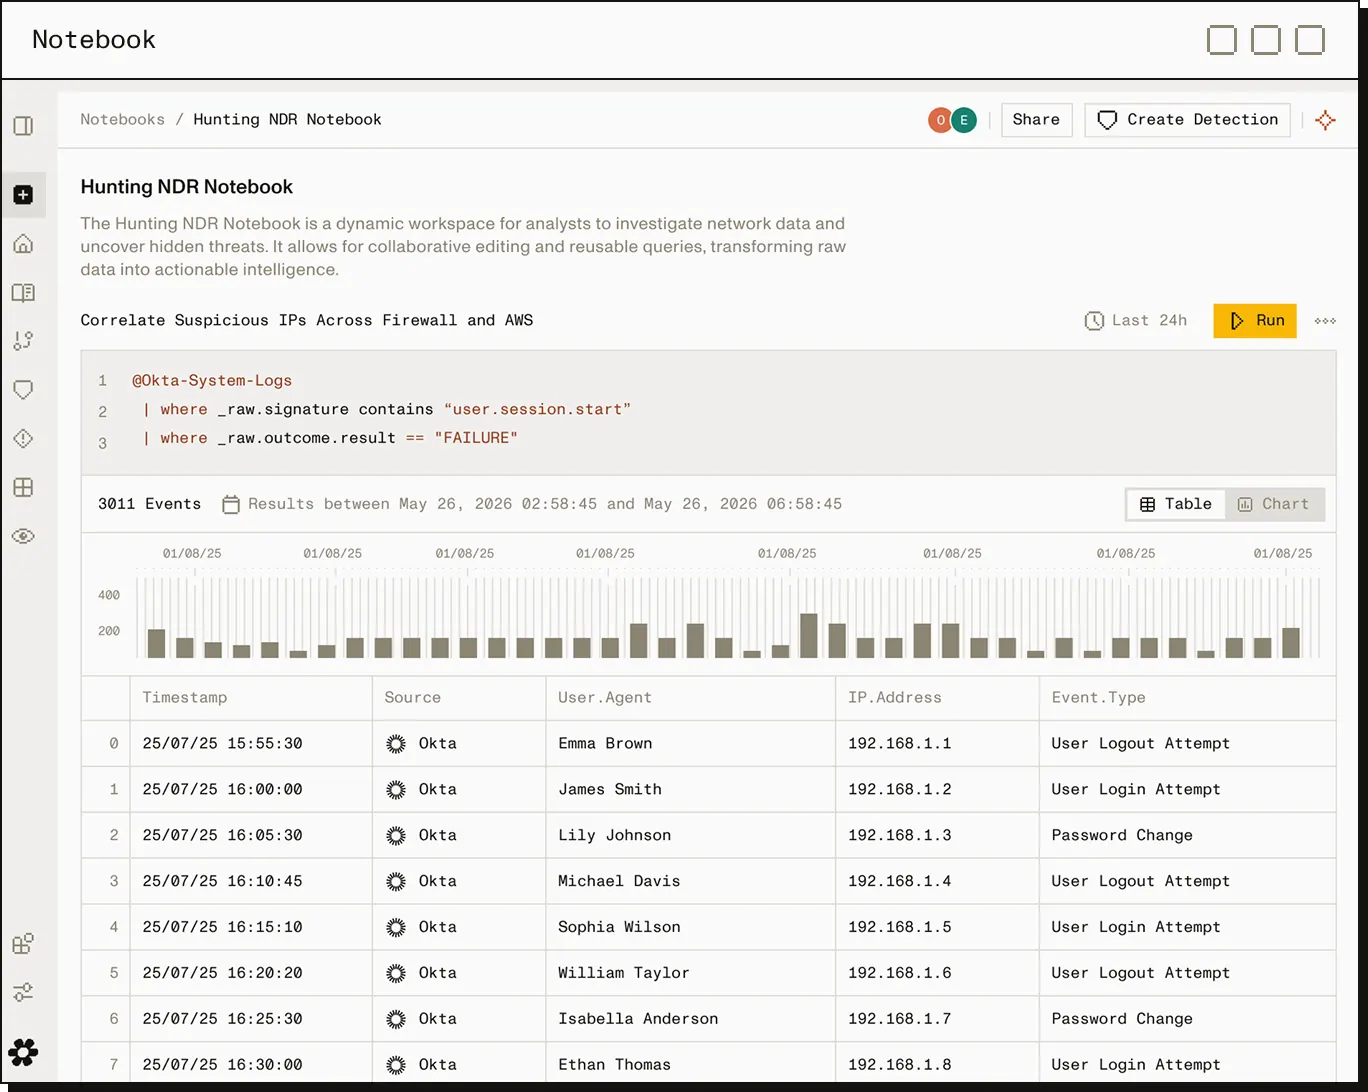
On Vega’s platform, the Security Analytics Mesh (SAM) runs AI-powered detection across all data sources without a migration. Analysts — or agents via MCP — can query any data with natural language, KQL, or Vega’s MCP, and build multi-cell notebooks as if every dataset were in the same place and the same OCSF schema. Vega’s wording: zero data migration, ingestion, or parsing.
SAM is also how Vega says teams can shift data to low-cost object storage across all three major clouds without giving up performance, analytics or detection, while keeping a single unified view. It layers onto the stack you already run, so you can keep a legacy SIEM and augment it, or retire it on your own timeline. Vega claims first value up to 36× faster than a legacy SIEM migration.
Product screens courtesy of Vega.
The figures below are published by Vega.
Search in plain language across all sources, in place.
Every detection finishes what it starts, then tunes the noisiest rules by 94.5%.
Versus legacy SIEM — no ingestion fees, no duplicate storage, no migration projects.
HackLabs breaks into organisations so they can build better defences — and we stay to help operate them. Agentic platforms like Vega let a small, skilled team run the full defensive loop. If you want to explore that shift, talk to us.
Offence-led cybersecurity, end to end. We have been helping Australian organisations defend themselves for nearly two decades.
Senior practitioners, not a junior queue. Detection and response advice informed by people who know how attackers actually operate.
No offshore subcontracting. Your data and your conversations stay with an Australian team — Sydney, Melbourne, Brisbane and Singapore.
From managed monitoring to incident response. Vega is one of the platforms we can help you assess as an alternative to legacy SIEM.
Performance figures on this page are published by Vega. vega.io
Tell us about your environment and we'll respond within one business day.
📅 Book a meeting with Chris